5.5.3. OPC DA
Connecting to an OPC DA server How-To

Connecting from an OPC DA client How-To
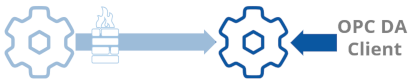
Tunnelling is the best way to network OPC DA. It avoids DCOM, which is difficult to configure and not very secure. For secure, isolated networks, you can make a traditional client-to-server connections, keeping all firewalls open. Over an insecure, exposed network, you can make an outbound connection, as shown above. This keeps all inbound firewall ports closed on the data source side, for zero attack surface.